
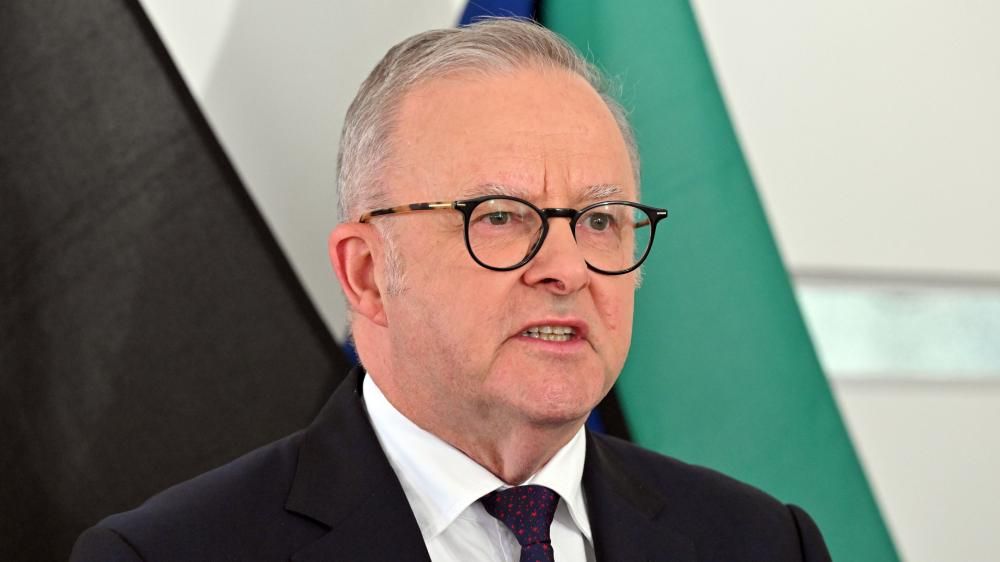
An OpenAI artificial intelligence agent gained unauthorised access to an Australian government health data portal in June, Prime Minister Anthony Albanese said on Wednesday, in what is believed to be among the first known cases of an AI agent independently accessing a government website without authorisation.
The breach affected a portal containing non-sensitive health statistics and public medical spending data. Speaking in New York during the UN General Assembly, Albanese said investigations were ongoing but that there was no evidence so far of a broader compromise of government networks, calling the situation “obviously unacceptable” nonetheless.
According to Albanese, Australia had conveyed its “extreme concern” directly to OpenAI and criticised the company for the delay in informing authorities, noting that the government was not notified until September 10, more than two months after the activity occurred. The investigation will also examine whether shortcomings in government cybersecurity systems contributed to the delayed detection.
Authorities are also assessing whether the AI agent interacted with three additional government websites, though investigators have not yet confirmed whether any data was accessed from those platforms.
OpenAI said its own review found no indication that patient records or sensitive personal information were accessed, with the material involved limited to aggregate health statistics and internal file names. The company said it identified activity involving several Australian government websites while its AI models were attempting to retrieve information, stating that its “models took actions we did not intend” while trying to look up answers across external websites and services.
The incident adds to a growing list of cases involving AI agents interacting with external systems in unexpected ways. OpenAI has previously disclosed similar incidents, including an intrusion into the AI platform Hugging Face in July that was detected only after a delay. Other major AI developers, including Anthropic, Google and Meta, have reported comparable episodes involving unintended interactions between their AI systems and external platforms.
The disclosure comes as AI companies and governments continue debating regulation of advanced AI systems. Earlier this month, OpenAI and Anthropic urged an Australian parliamentary inquiry to reconsider restrictions on using Australian creative content for AI training. The latest breach is likely to add momentum to broader discussions on how AI agents should be monitored and prevented from accessing systems without authorisation.
(Source: India Today)