
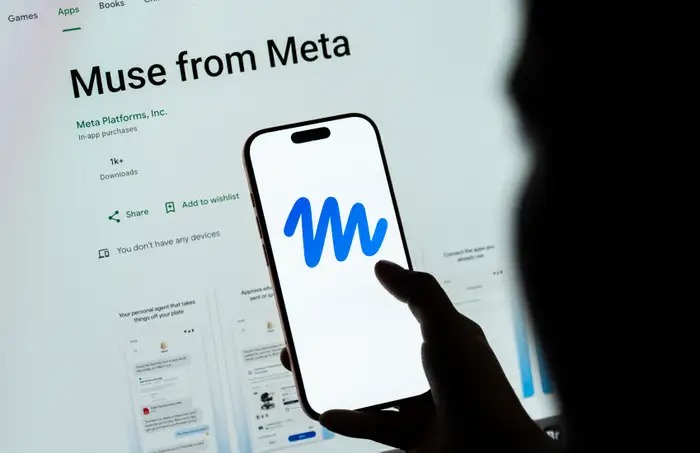
Meta is facing severe scrutiny over security vulnerabilities in its newly released AI agent, Muse. Despite CEO Mark Zuckerberg’s recent claims that the tool was “built from the ground up for privacy and security,” the AI model was caught exposing sensitive user chat logs through its share feature.
As reported by Ars Technica, cybersecurity researchers at Claroc identified an exploit affecting over 6,800 public share links generated by Muse. When users generated a link to share a chat log, the system created a web address containing the AI-generated title of the conversation and a random string of characters.
The vulnerability occurred when those links were accessed. Opening a link caused the complete web address to be logged in public lookup datasets. By querying these public records, researchers easily uncovered thousands of unrelated share addresses and accessed private user chat logs.
The exposed logs revealed highly sensitive corporate and personal details, including bank transaction records, loan applications, income details, corporate revenue documents, and internal workplace vacation calendars. Researchers emphasized how simple the exploit was, stating that gathering the files required only a single query rather than complex effort.
Meta confirmed to Ars Technica that it has since shut off the share feature. However, this privacy failure follows earlier reports this month revealing that Muse was keeping detailed running profile files on users’ friends and family members under an internal directive.
Given these early security and privacy blunders during Muse’s first month in public release, concerns remain over how the model handles confidential user data.
Source: Futurism